Verify a certificate by scanning its QR code or uploading a photo
The public verify page opens the camera, reads the QR code, and takes you to the certificate. You can also upload a photo when a scan is not practical.
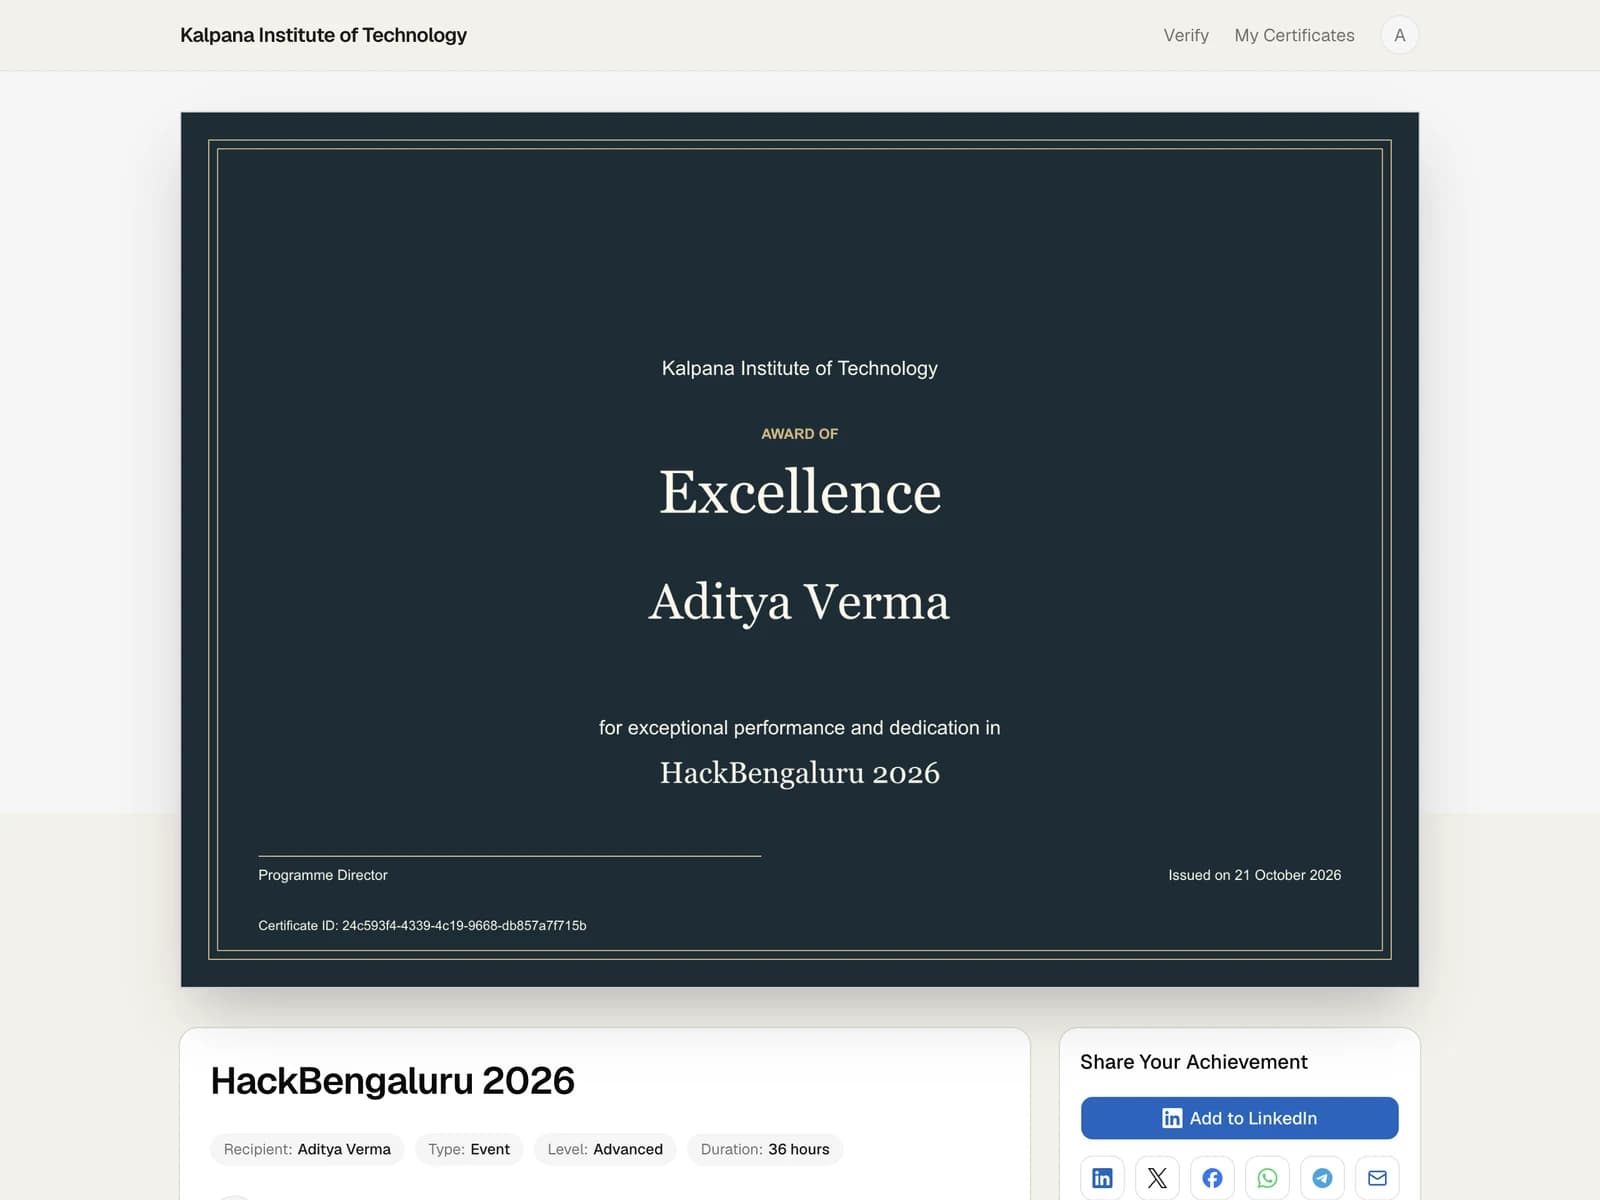
A printed certificate usually arrives as a photograph, a scan, or a PDF attachment. The person checking it should not have to retype a long credential ID to find out whether it is real.
The public verification page now reads the QR code directly.
What changed
- Camera scanning. Open the verify page, point the camera at the QR code on a printed certificate, and the certificate page opens once the code is read.
- Image upload. If the certificate is already a photo, a screenshot, or an exported file, upload it instead. The decoder finds the QR code inside the full image, not just a cropped square.
- The same validation path. The code is decoded in the browser, then checked against the public API before the certificate is shown. A QR code that points somewhere else does not become a valid certificate.
Why it matters
Verification is the part of the credential the recipient actually experiences after the event. It should work from a phone camera, a printed award on a wall, or a certificate someone forwarded as an image. Scanning removes the step where a name or ID gets mistyped, and it gives the person checking the certificate a clear answer in one action.
The QR code is still optional on the design. If a certificate does not carry one, the public page can be reached from its link, and the certificate ID can still be checked directly.
Related